GreyNoise Intelligence Review
GreyNoise Intelligence is a powerful software tool designed to help organizations identify and mitigate noise in their network environments. With its extensive database of internet-wide scan and attack data, GreyNoise provides valuable insights into the security posture of an organization, helping security teams prioritize and respond to real threats.
Key Takeaways
- GreyNoise Intelligence helps organizations differentiate between legitimate and malicious internet traffic.
- The software provides context to assist security teams in identifying and focusing on real threats.
- GreyNoise can integrate with existing security tools and workflows to enhance overall security posture.
- The platform offers a comprehensive API for seamless integration with other security solutions.
- GreyNoise Intelligence is a valuable asset for threat intelligence teams, SOC analysts, and incident response teams.
Table of Features
| Feature | Description |
|---|
| Noise Detection | Identifies and filters out non-malicious internet noise. |
| Contextual Information | Provides valuable context to help prioritize real threats. |
| Integration Capabilities | Can seamlessly integrate with existing security tools. |
| Extensive Database | Maintains a vast database of internet-wide scan and attack data. |
| API Support | Offers a comprehensive API for integration with other solutions. |
Use Cases
1. Threat Intelligence Analysis
GreyNoise Intelligence is an invaluable tool for threat intelligence teams. By analyzing internet-wide scan and attack data, it helps identify potential threats and provides context to prioritize and respond effectively.
2. Security Operations Center (SOC) Analysis
SOC analysts can leverage GreyNoise to differentiate between legitimate and malicious traffic, reducing false positives and enabling faster response times to real threats. It enhances the overall efficiency of security operations.
3. Incident Response
During incident response, GreyNoise Intelligence provides critical information and insights to understand the nature of an attack and determine appropriate mitigation strategies. It enables incident response teams to make informed decisions quickly.
Pros
- Noise Detection: GreyNoise effectively filters out non-malicious internet noise, reducing false positives and enabling security teams to focus on real threats.
- Contextual Information: The software provides valuable context about identified threats, helping prioritize incidents and take appropriate actions.
- Integration Capabilities: GreyNoise seamlessly integrates with existing security tools and workflows, enhancing overall security posture without disrupting established processes.
- Extensive Database: The platform maintains a vast and constantly updated database of internet-wide scan and attack data, ensuring accurate threat identification.
- API Support: GreyNoise offers a comprehensive API, allowing easy integration with other security solutions and enabling customized workflows.
Cons
- Complexity: The software may have a steep learning curve for users who are not familiar with threat intelligence analysis or incident response processes. Adequate training and documentation are recommended.
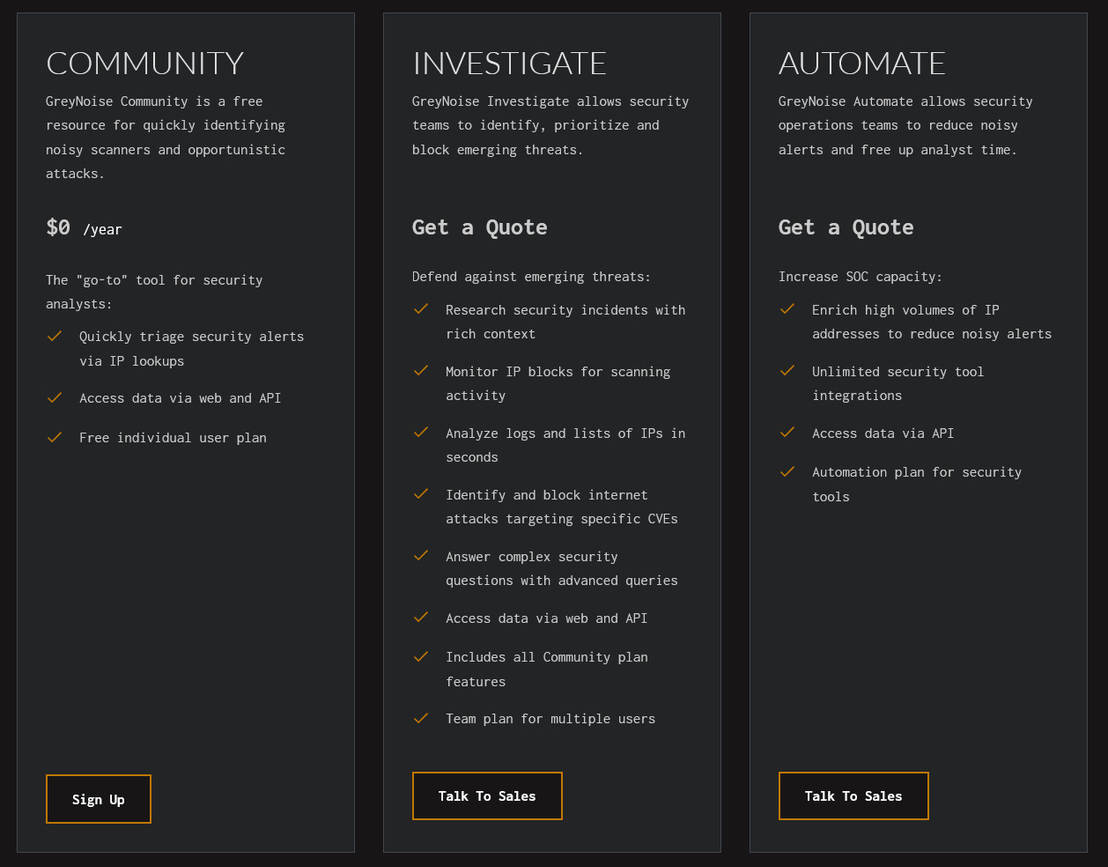
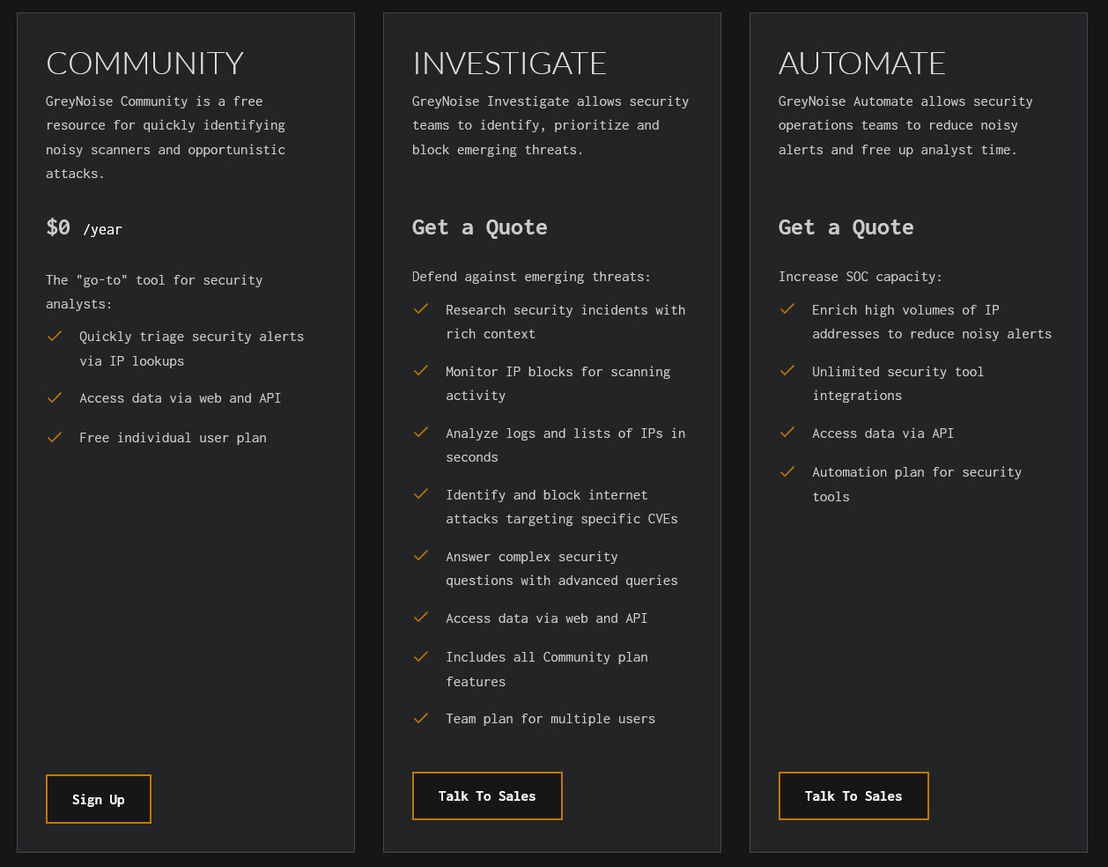
- Cost: GreyNoise Intelligence is a premium software, and the pricing model may not be suitable for small organizations or those with limited security budgets.
Recommendation
GreyNoise Intelligence is an exceptional tool for organizations seeking to improve their security posture and identify real threats in their network environment. With its powerful noise detection capabilities, extensive database, and seamless integration options, GreyNoise is a valuable asset for threat intelligence teams, SOC analysts, and incident response teams. While the software may require some initial investment in training and resources, the benefits it provides in terms of reduced false positives and faster incident response make it well worth considering for organizations serious about their security.