GreyNoise Intelligence: Unveiling the Noise in Cybersecurity
Introduction
In today's digital landscape, organizations face an ever-increasing number of cybersecurity threats. Identifying and mitigating these threats is essential for safeguarding sensitive data and ensuring business continuity. GreyNoise Intelligence, a powerful cybersecurity platform, offers a unique approach to managing the noise and improving threat intelligence. In this comprehensive review, we will explore the features, use cases, pros, and cons of GreyNoise Intelligence, providing valuable insights to help you make an informed decision.
Key Takeaways
- GreyNoise Intelligence is a robust cybersecurity platform that helps organizations identify and filter out benign scanning and internet background noise.
- By filtering out noise, GreyNoise allows security teams to focus on genuine threats and significantly reduces false positives.
- The platform offers a vast collection of internet-wide scan data and insights, enabling users to gain a deeper understanding of the global threat landscape.
- GreyNoise Intelligence is a valuable tool for threat intelligence analysts, incident response teams, and security operation centers (SOCs), enhancing their ability to detect and respond to cyber threats effectively.
Table of Features
| **Feature** | **Description** |
|---|
| Noise Reduction | GreyNoise identifies and filters out benign scanning activity and internet background noise, allowing security teams to focus on genuine threats and reducing false positives. |
| Internet-Wide Scan Data | The platform offers a vast collection of internet-wide scan data, providing valuable insights into the global threat landscape. |
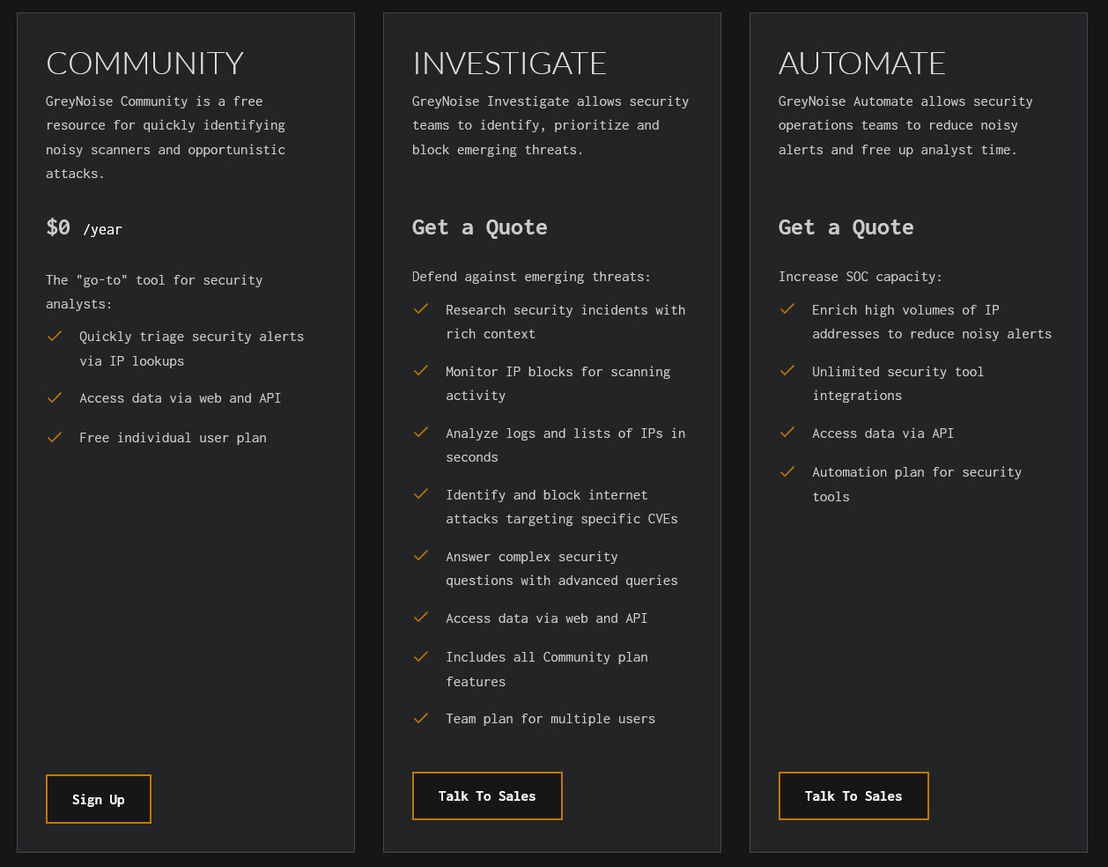
| API Access | GreyNoise Intelligence provides an API that allows users to integrate its functionality into existing security tools and systems, enhancing threat intelligence capabilities. |
| Threat Intelligence | The platform offers comprehensive threat intelligence, enabling users to gain insights into malicious activity, identify trends, and enhance their overall cybersecurity posture. |
| Real-Time Alerts | GreyNoise provides real-time alerts for specific threat indicators, empowering security teams to respond swiftly and mitigate potential risks. |
| Customizable Dashboards | Users can create customized dashboards to visualize and monitor specific threat intelligence metrics and trends, providing a tailored view of the threat landscape. |
| Collaboration Tools | The platform offers collaboration features, allowing teams to share threat intelligence, collaborate on investigations, and enhance their collective defense against cyber threats. |
| Historical Data Access | GreyNoise allows users to access historical data, enabling them to perform in-depth analysis, track threat trends over time, and enhance their understanding of evolving attack patterns. |
Use Cases
GreyNoise Intelligence can be leveraged in various use cases, including:
- Threat Intelligence Analysis: GreyNoise provides comprehensive threat intelligence, allowing analysts to identify and investigate malicious activity, track threat trends, and make informed decisions.
- Incident Response: The platform's real-time alerts enable incident response teams to swiftly respond to potential threats, minimizing the impact of cyber incidents and accelerating the recovery process.
- Vulnerability Management: GreyNoise helps security teams prioritize vulnerability remediation efforts by filtering out benign scanning, focusing on genuine threats, and reducing alert fatigue.
- Security Operation Centers (SOCs): GreyNoise enhances SOC capabilities by providing valuable insights into the global threat landscape, enabling proactive threat hunting, and improving incident response effectiveness.
Pros
- Noise Reduction: GreyNoise's ability to filter out benign scanning and internet background noise is invaluable for improving the efficiency of security teams, eliminating false positives, and focusing on genuine threats.
- Extensive Internet-Wide Scan Data: The platform's vast collection of internet-wide scan data provides unique insights into the global threat landscape, enabling users to gain a deeper understanding of evolving attack patterns.
- API Access: GreyNoise's API allows for seamless integration with existing security tools and systems, enhancing threat intelligence capabilities and streamlining workflows.
- Real-Time Alerts: The platform's real-time alerting feature empowers security teams to respond swiftly to potential threats, minimizing the impact of cyber incidents and reducing the time to detect and respond.
- Customizable Dashboards: GreyNoise enables users to create personalized dashboards, visualizing specific threat intelligence metrics, and trends, providing a tailored view of the threat landscape.
- Collaboration Tools: The platform's collaboration features foster teamwork, enabling teams to share threat intelligence, collaborate on investigations, and strengthen their collective defense against cyber threats.
Cons
- Learning Curve: GreyNoise Intelligence is a sophisticated platform that may require some time for users to familiarize themselves with its features and optimize its potential.
- Resource Intensive: The vast amount of internet-wide scan data collected by GreyNoise may require significant storage and computational resources, particularly for organizations with limited infrastructure.
Recommendation
GreyNoise Intelligence is a flagship cybersecurity platform that effectively filters out noise, improves threat intelligence, and enhances incident response capabilities. Its comprehensive threat intelligence, real-time alerts, and collaboration features make it an invaluable tool for organizations looking to strengthen their cybersecurity posture. While there may be a slight learning curve and resource considerations, the benefits of using GreyNoise Intelligence outweigh these limitations. We highly recommend GreyNoise Intelligence to organizations of all sizes, particularly those with a strong focus on proactive security and incident response.