Overview
Explain what open-appsec is and how it operates. In traditional WAFs, continuous learning is crucial for accurate detection. This involves automating the installation, configuration, and upgrades. Cloud native CI/CD friendly deployment and automation simplify and streamline this process using Helm Charts, Kubernetes Annotations, Terraform, or extensive GraphQL API. As a result, manual fine-tuning and exception creation, typically needed with traditional WAFs, are eliminated, enabling fast and precise detection. Cloud native CI/CD-friendly deployment and automation allow for effortless automation and deployment.
Expert review of open-appsec
Review: open-appsec
Key Takeaways:
- open-appsec is an open-source software for application security testing.
- It provides a comprehensive set of security testing tools and libraries.
- The software enables developers to identify and fix vulnerabilities in their applications.
- open-appsec is highly extensible and customizable, allowing integration with existing CI/CD pipelines.
- It offers excellent documentation and community support for users.
- The software is suitable for both small and large development teams.
Table of Features:
| Feature | Description |
|---|---|
| Security Testing Tools | Provides a wide range of security testing tools and libraries. |
| Vulnerability Scanning | Identifies and reports vulnerabilities in applications. |
| Secure Code Analysis | Analyzes source code for potential security vulnerabilities. |
| Integration | Can be integrated into existing CI/CD pipelines for automated security testing. |
| Extensibility | Highly customizable and extensible to accommodate specific needs. |
| Documentation | Offers comprehensive documentation for easy implementation and usage. |
| Community Support | Benefit from an active community for assistance and knowledge sharing. |
Use Cases:
- Security Testing: open-appsec is primarily designed for security testing of applications. It allows developers to identify vulnerabilities and ensure robust security measures.
- Vulnerability Management: The software enables developers to scan and report vulnerabilities in their applications. It helps in prioritizing and fixing potential security risks.
- Secure Code Analysis: open-appsec's code analysis tools assist developers in identifying potential security vulnerabilities in their source code.
- CI/CD Integration: The software can be seamlessly integrated into existing CI/CD pipelines, allowing for automated security testing throughout the development process.
Pros:
- Comprehensive Security Testing: open-appsec offers a comprehensive set of security testing tools, including vulnerability scanning and secure code analysis. This allows developers to cover multiple aspects of application security.
- Extensibility: The software can be easily customized and extended to meet specific security testing requirements. Developers can integrate additional tools or build their own modules.
- Documentation: open-appsec provides extensive documentation, making it easier for users to understand and implement the software effectively.
- Community Support: The open-appsec community is active and supportive, providing assistance, sharing knowledge, and contributing to the software's development.
- Integration with CI/CD Pipelines: The software seamlessly integrates with existing CI/CD pipelines, enabling automated security testing as part of the development process.
Cons:
- Learning Curve: open-appsec may have a steep learning curve for users who are not familiar with application security testing tools and concepts.
- Limited User Interface: The software primarily functions through a command-line interface, which might not be suitable for users who prefer a graphical user interface.
- Lack of Enterprise Support: As an open-source software, open-appsec may not offer dedicated enterprise support or service level agreements that some organizations may require.
Recommendation:
open-appsec is an excellent open-source software for application security testing. It provides a comprehensive set of security testing tools and libraries, allowing developers to identify and fix vulnerabilities in their applications. The software's extensibility and integration capabilities make it suitable for both small and large development teams. Although there may be a learning curve for users new to application security testing, the extensive documentation and active community support ensure a smooth learning experience. However, organizations seeking enterprise-level support may need to consider other commercial solutions. Overall, open-appsec is a valuable asset for any development team aiming to enhance the security of their applications.
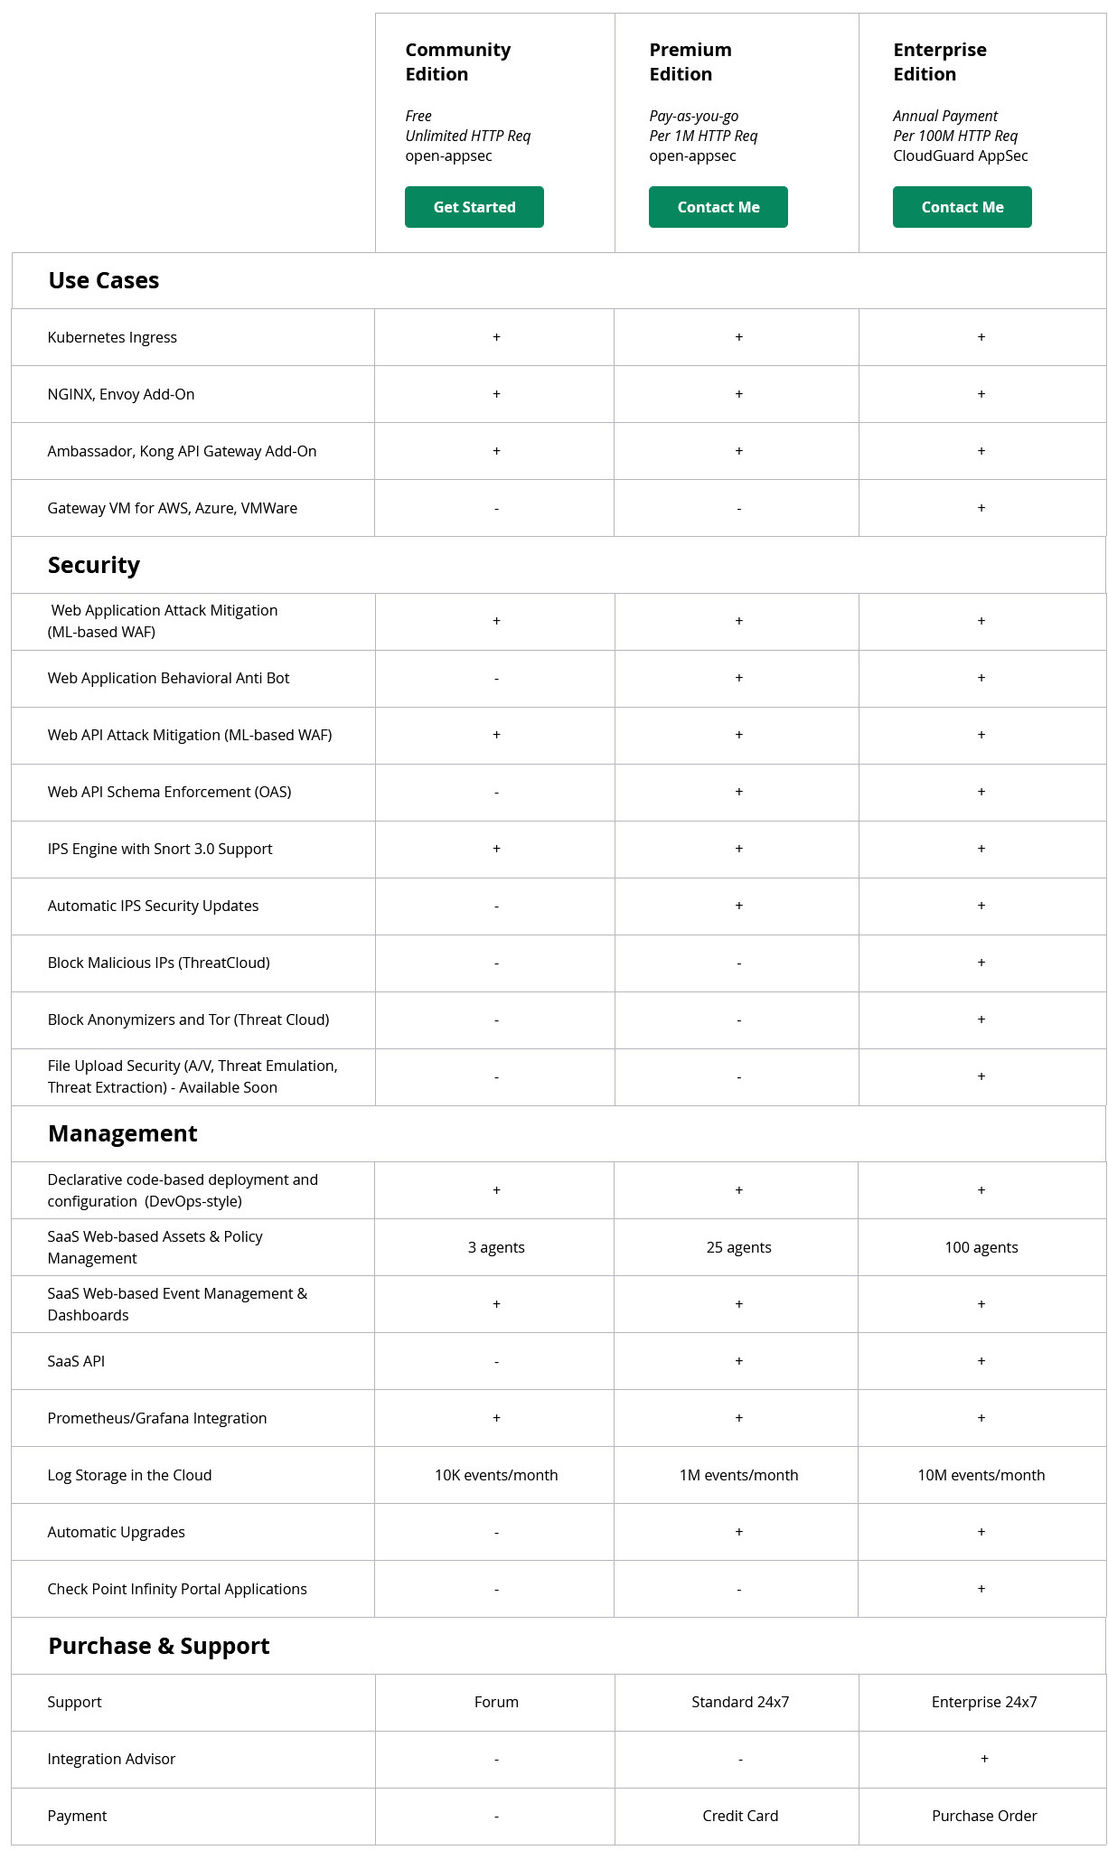
open-appsec pricing model
Freemium , Quotation Based
Technical details
- Support: Online
- Customer Type: Large Enterprises Medium Business Small Business
- Location / Phone Number: San Carlos, California / +1-800-429-4391
- Deployment: SaaS/Web/Cloud
- Official Website: https://www.openappsec.io/
- Category: Machine Learning Software
Related software
Apibit summaries are researched from vendor documentation and public information. Features and prices change often, so confirm details with the vendor. See our editorial policy and advertiser disclosure.