Overview
What is the purpose and functioning of CanIPhish? CanIPhish is a Secure Email Gateway evaluation toolkit that is open-sourced. The platform integrates with public domain tools to detect and exploit vulnerabilities in real-world situations. It offers various features, including advanced phishing libraries, easy campaign setup, extensive documentation, adaptable infrastructure, and more.
Expert review of CanIPhish
Review: CanIPhish
Introduction
CanIPhish is a powerful software tool designed for ethical hackers and security professionals to assess the vulnerability of online systems to phishing attacks. With its comprehensive features and user-friendly interface, it offers a range of capabilities that enable users to simulate phishing attacks, identify vulnerabilities, and strengthen their defenses against cyber threats. In this review, we will explore CanIPhish in detail, examining its key features, use cases, pros, and cons.
Key Takeaways
- CanIPhish is a robust software tool for simulating phishing attacks and assessing the vulnerability of online systems.
- It provides users with a user-friendly interface, making it accessible to both beginners and experienced security professionals.
- With its comprehensive set of features, CanIPhish allows users to perform various types of phishing attacks, including credential harvesting, spear phishing, and clone phishing.
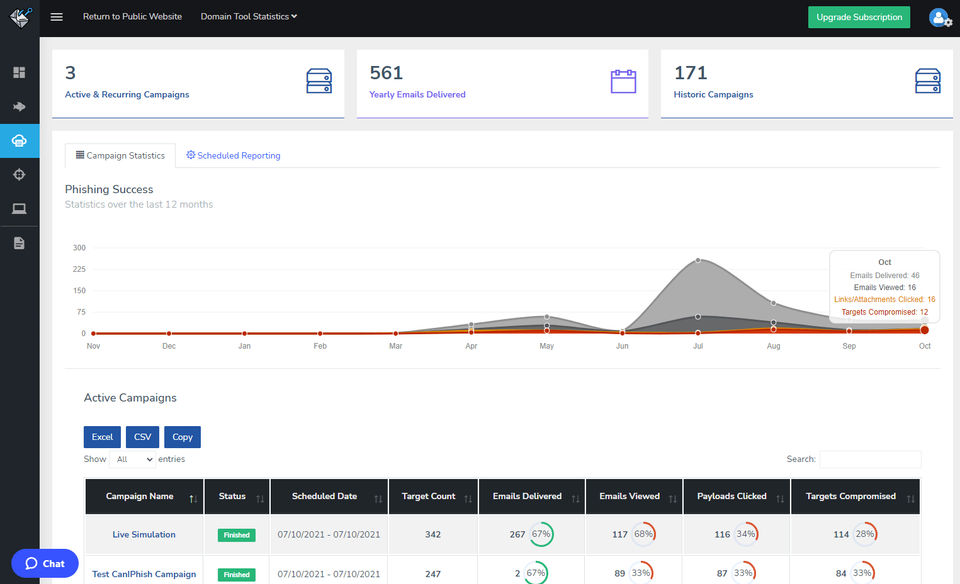
- The software provides detailed reports and analytics, enabling users to identify weaknesses and improve their security measures.
- CanIPhish offers integration capabilities with popular security tools, enhancing its functionality and compatibility.
- While the software is primarily used for ethical hacking purposes, it requires responsible usage to avoid any malicious activities.
Table of Features
Below is a table summarizing the key features of CanIPhish:
| Feature | Description |
|---|---|
| Phishing Attack Types | Allows for simulation of various phishing attack types, including spear phishing, credential harvesting, and clone phishing. |
| User-Friendly Interface | Intuitive and easy-to-use interface, suitable for both beginners and experienced security professionals. |
| Reporting and Analytics | Generates detailed reports and analytics, providing valuable insights for vulnerability assessment and improvement. |
| Integration Capabilities | Offers integration with popular security tools, enhancing functionality and compatibility. |
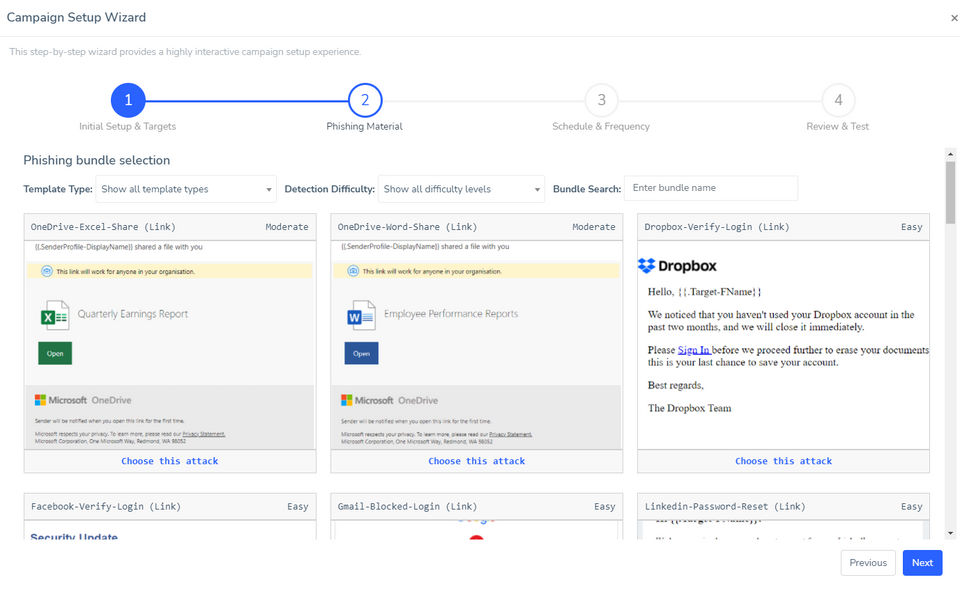
| Phishing Campaigns | Enables users to create and manage multiple phishing campaigns simultaneously. |
| Email Templates | Provides a library of pre-designed email templates for efficient phishing simulations. |
| URL Cloning | Allows for the cloning of legitimate websites to create convincing phishing pages. |
| Credential Harvesting | Provides options to harvest and analyze user credentials to assess susceptibility. |
| Two-Factor Authentication | Supports testing the effectiveness of two-factor authentication mechanisms. |
| Training and Education | Offers educational resources and training modules to enhance user knowledge and awareness. |
Use Cases
CanIPhish can be utilized in various scenarios to assess and improve the security posture of online systems. Here are a few notable use cases:
- Penetration Testing: CanIPhish is an invaluable tool for security professionals during penetration testing engagements. It enables them to identify vulnerabilities, evaluate the effectiveness of security controls, and provide actionable recommendations to enhance an organization's security infrastructure.
- Employee Awareness Training: Many organizations use CanIPhish as part of their employee awareness training programs. By simulating phishing attacks and tracking user responses, organizations can educate their employees about potential risks, enhance their awareness, and promote safer online practices.
- Security Audits: CanIPhish assists in conducting comprehensive security audits by identifying weak links in an organization's security architecture. By simulating real-world phishing attacks, the software helps auditors evaluate the effectiveness of existing security measures and recommend improvements.
- Policy Validation: Organizations can leverage CanIPhish to assess the effectiveness of security policies and procedures. By testing the response of employees to phishing attacks, organizations can evaluate if their policies are being properly followed and identify areas for improvement.
Pros
- User-Friendly Interface: CanIPhish offers a well-designed and intuitive user interface, making it accessible to security professionals of all levels of expertise.
- Comprehensive Phishing Attack Types: The software provides a wide range of phishing attack types, allowing users to simulate various real-world scenarios.
- Detailed Reports and Analytics: CanIPhish generates detailed reports and analytics, enabling users to identify vulnerabilities and track improvements over time.
- Integration Capabilities: The software seamlessly integrates with popular security tools, enhancing its functionality and compatibility within existing security infrastructures.
- Training and Education: CanIPhish provides educational resources and training modules to help users enhance their knowledge and awareness of phishing threats and mitigation strategies.
Cons
- Ethical Usage Responsibility: CanIPhish, like any other hacking tool, requires responsible and ethical usage to avoid any malicious activities. Users must ensure that they comply with legal and ethical guidelines while using the software.
- Learning Curve for Beginners: While CanIPhish offers a user-friendly interface, beginners in the field of ethical hacking might still require some time to familiarize themselves with the tool's functionalities and settings.
Recommendation
CanIPhish is a powerful and comprehensive software tool that enables ethical hackers and security professionals to assess the vulnerability of online systems to phishing attacks. With its user-friendly interface, wide range of phishing attack types, detailed reporting, and integration capabilities, it offers a valuable solution for organizations aiming to strengthen their security posture. However, it is important to emphasize the responsible and ethical usage of CanIPhish to avoid any misuse or potential harm. With proper training and adherence to ethical guidelines, CanIPhish can be an excellent addition to a security professional's toolkit.
CanIPhish pricing model
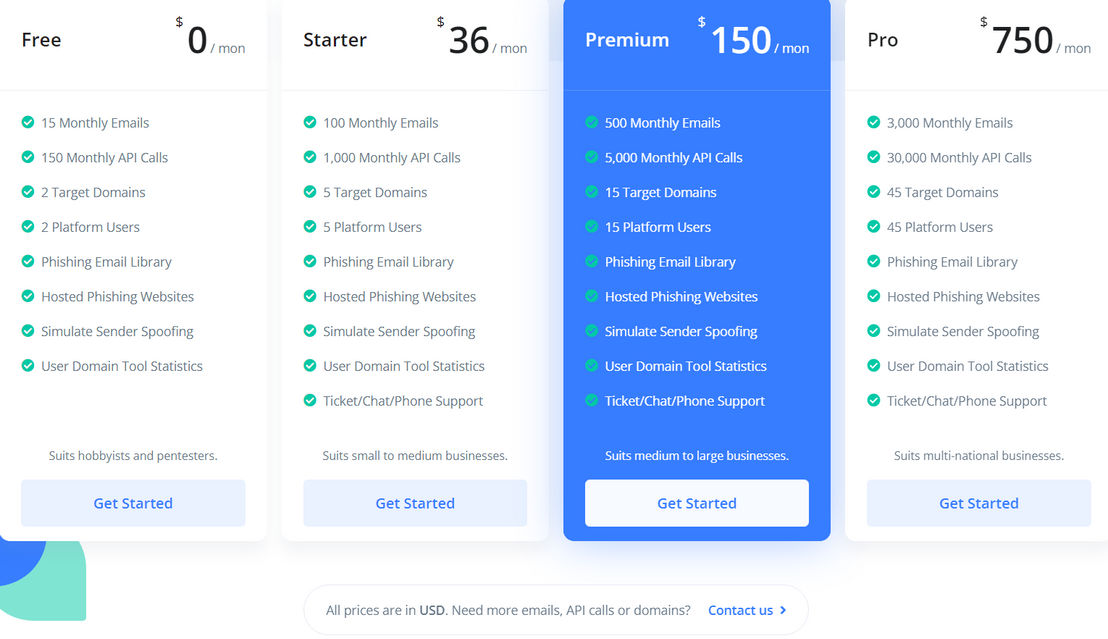
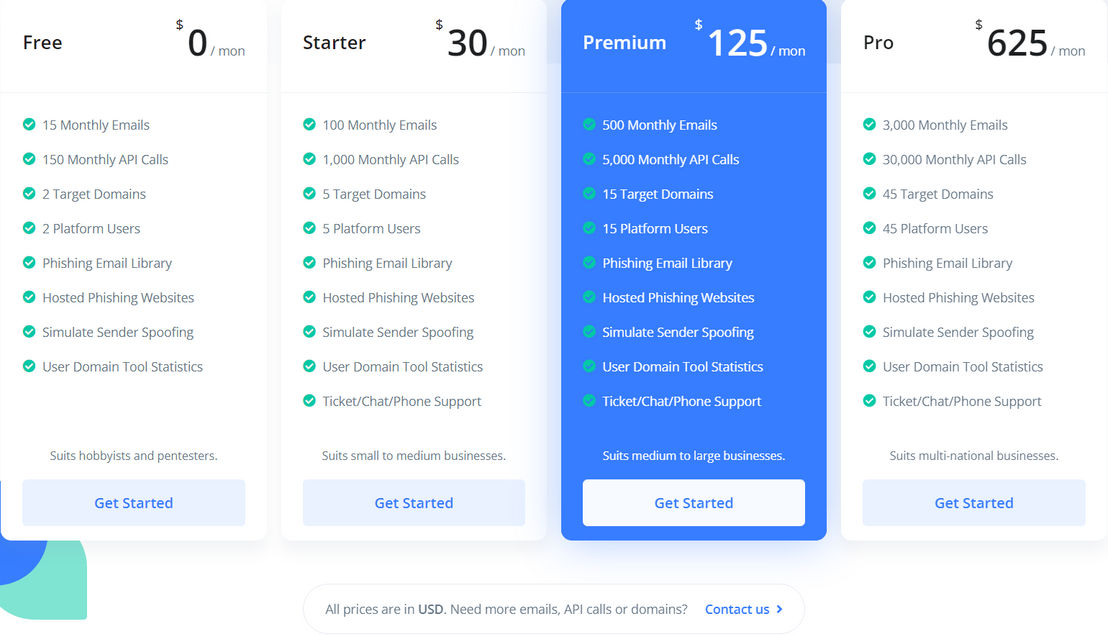
Freemium , Subscription , Quotation Based
Screenshots
Technical details
- Support: Online
- Customer Type: Large Enterprises Medium Business Small Business
- API
- Location / Phone Number: Sydney New South Wales
- Australia
- Deployment: SaaS/Web/Cloud
- Official Website: https://caniphish.com/
- Category: Security Awareness Training Software
Related software
Apibit summaries are researched from vendor documentation and public information. Features and prices change often, so confirm details with the vendor. See our editorial policy and advertiser disclosure.