Overview
What is the purpose and functionality of Azure Sentinel? Azure Sentinel is a sophisticated security solution offered by Microsoft that offers a holistic perspective on potential threats, empowering organizations to identify and mitigate them. By utilizing cloud-native technology and scalability, Azure Sentinel enables efficient detection and monitoring of security alerts, proactive searching for threats, and automated response to security incidents. It eliminates the requirement for setting up and maintaining security infrastructure, allowing organizations to concentrate on effectively responding to threats. Azure Sentinel also delivers improved threat intelligence throughout the organization, enabling users to promptly and efficiently identify and address threats.
Expert review of Azure Sentinel
Azure Sentinel Review
Azure Sentinel is a cloud-native Security Information and Event Management (SIEM) solution developed by Microsoft. It provides organizations with a centralized platform for collecting, analyzing, and responding to security events and threats across their entire network. This review explores the key features, use cases, pros, cons, and provides a recommendation for adopting Azure Sentinel.
Key Takeaways
- Azure Sentinel is a cloud-native SIEM solution that offers advanced security analytics and threat intelligence capabilities.
- It integrates seamlessly with other Microsoft cloud services, allowing organizations to leverage their existing infrastructure and investments.
- With its scalability and flexibility, Azure Sentinel enables organizations to effectively detect, investigate, and respond to security threats in real-time.
- The solution leverages artificial intelligence and machine learning technologies to automate threat detection and response, reducing the burden on security analysts.
- Azure Sentinel provides a rich set of pre-built connectors, allowing organizations to collect security data from various sources, both on-premises and in the cloud.
- The solution offers extensive customization options, enabling organizations to tailor the platform to their specific security requirements.
Table of Features
| Feature | Description |
|---|---|
| Cloud-native | Azure Sentinel is built on the Azure cloud platform, providing scalability, reliability, and flexibility. |
| Advanced analytics | The solution utilizes AI and machine learning to detect and respond to security threats in real-time. |
| Threat intelligence | Azure Sentinel incorporates threat intelligence feeds to enhance threat detection capabilities. |
| Pre-built connectors | The platform offers a wide range of pre-built connectors for collecting security data from various sources. |
| Customization options | Organizations can customize Azure Sentinel to align with their specific security requirements. |
| Automation | The solution automates routine security tasks, freeing up security analysts to focus on critical threats. |
| Integration with Azure | Azure Sentinel seamlessly integrates with other Microsoft Azure services, simplifying deployment and management. |
Use Cases
- Threat detection and investigation: Azure Sentinel enables organizations to identify and respond to security threats in real-time. By analyzing security events and logs across the network, it detects suspicious activities, allowing security teams to promptly investigate and mitigate potential risks.
- Compliance management: Azure Sentinel provides organizations with the tools to meet regulatory compliance requirements. It offers built-in compliance dashboards and reports that help organizations monitor and report on security incidents, ensuring adherence to industry standards.
- Incident response: The solution streamlines incident response processes by automating repetitive tasks and providing security analysts with actionable insights. It enables organizations to effectively contain and remediate security incidents, minimizing the impact on business operations.
- Threat hunting: Azure Sentinel empowers security analysts to proactively search for potential threats and vulnerabilities within their network. By leveraging advanced analytics and machine learning, it helps uncover hidden patterns and indicators of compromise that may have been missed by traditional security controls.
Pros
- Seamless integration with other Microsoft Azure services, enhancing the overall security posture of organizations already leveraging the Azure ecosystem.
- Scalable and flexible architecture that accommodates organizations of all sizes, from small businesses to large enterprises.
- Advanced analytics and machine learning capabilities enable real-time threat detection and response, reducing manual effort and improving efficiency.
- Rich set of pre-built connectors facilitate the collection of security data from various sources, simplifying the onboarding process.
- Extensive customization options allow organizations to tailor Azure Sentinel to their specific security requirements, ensuring maximum effectiveness.
Cons
- Certain advanced features may require additional configuration and expertise, potentially posing a challenge for organizations without dedicated security teams.
- The learning curve for new users can be steep, requiring time and resources for training and familiarization with the platform.
- While Azure Sentinel integrates well with other Microsoft services, integration with third-party solutions may require additional development effort.
Recommendation
Based on its comprehensive features, integration capabilities, and advanced analytics, Azure Sentinel is a highly recommended SIEM solution for organizations looking to strengthen their security posture. It offers a flexible and scalable platform that can adapt to the evolving threat landscape and effectively detect and respond to security incidents in real-time. However, organizations should consider the need for dedicated security expertise and allocate resources for training and onboarding to fully leverage the solution's capabilities.
Azure Sentinel pricing model
Quotation Based
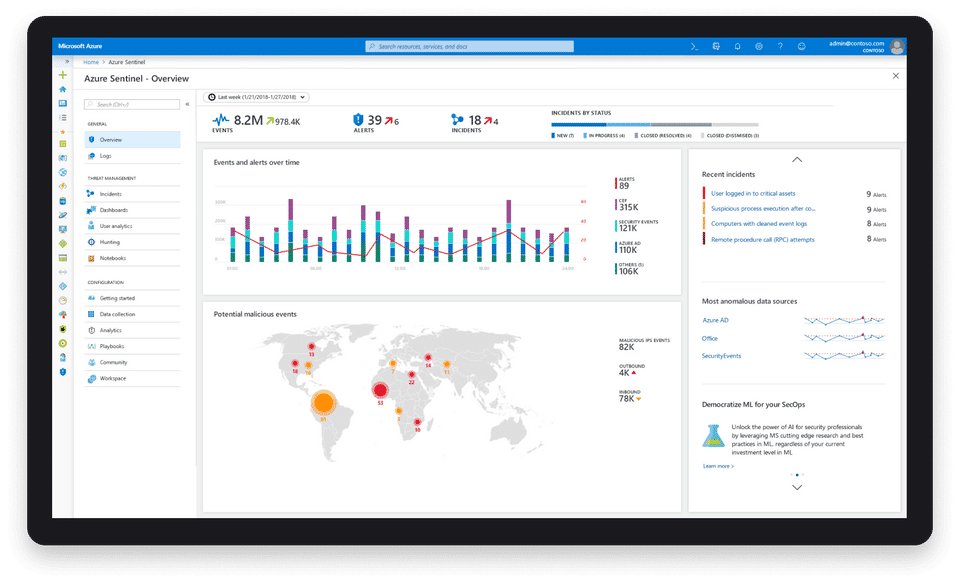
Screenshots
Technical details
- Support: Online
- Customer Type: Large Enterprises Medium Business Small Business
- API
- Location / Phone Number: Redmond, Washington State
- Deployment: SaaS/Web/Cloud
- Official Website: https://azure.microsoft.com/en-us/services/azure-sentinel/
- Category: Security Orchestration, Automation, and Response (SOAR) Software
Related software
Apibit summaries are researched from vendor documentation and public information. Features and prices change often, so confirm details with the vendor. See our editorial policy and advertiser disclosure.